





 systemd-journal Logs Management
Query Terabytes of Logs in Seconds - Without Moving a Single Byte
Netdata transforms systemd-journal log management by querying logs directly where they live. Eliminate expensive log pipelines, get sub-2-second query latency, and troubleshoot with AI-powered insights - all while keeping your data sovereign and secure on your infrastructure.

Why Netdata Transforms systemd-journal Management
The only solution that queries logs directly at the edge - no pipelines, no duplication, no delays
Sub-2-Second Queries
Query terabytes of journal data in seconds with intelligent sampling that evaluates 1M entries - 200× more than competitors - ensuring high accuracy at any scale.
90% Cost Reduction
Eliminate expensive log pipelines and storage infrastructure. No Elasticsearch, no Splunk, no data duplication - just direct access to your existing journal files.
AI-Powered Troubleshooting
Ask your AI assistant natural language questions about logs via Model Context Protocol. Get instant root cause analysis correlated with metrics and anomalies.
Zero Configuration
Production-ready in 60 seconds. Auto-discovers all journal sources, generates interactive dashboards, and provides point-and-click filtering - no query languages required.
Unified Metrics + Logs
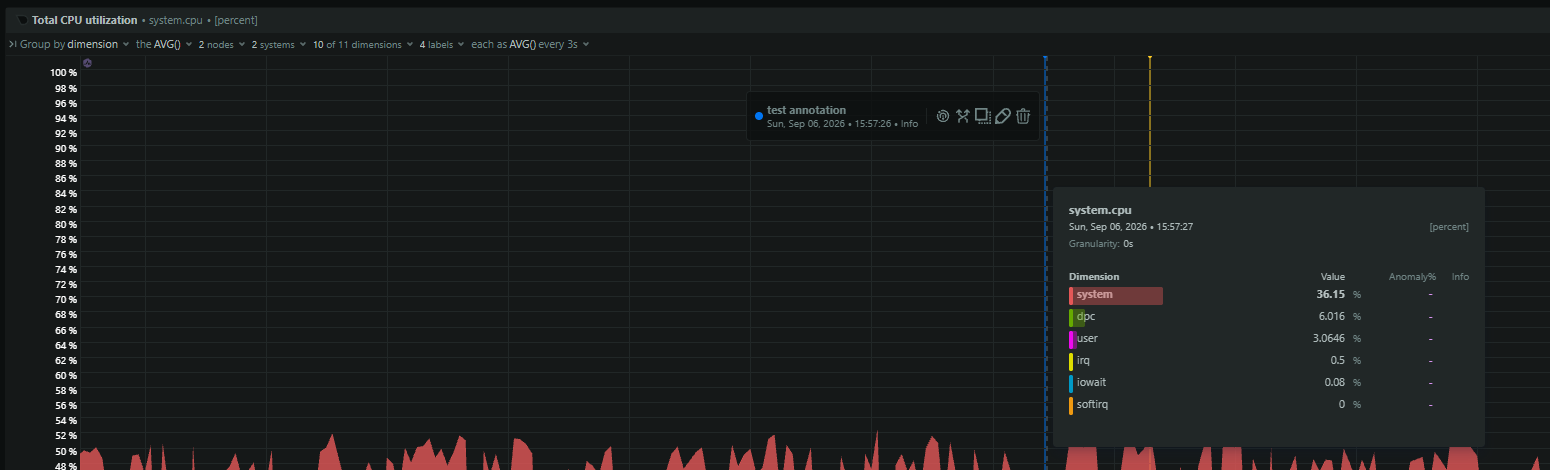
See CPU spikes in metrics, click the timeframe, and logs automatically filter to that exact moment. Correlation is instant and visual - no context switching between tools.
Data Sovereignty by Design
Logs never leave your infrastructure. Query journals in place with read-only access, FSS tamper detection support, and TLS encryption for centralization.
Trusted by DevOps teams managing millions of journal entries daily








Transform How You Work with systemd-journal Logs
Troubleshoot at the Speed of Thought
Sub-2-second query latency
Experience Real-Time Logs

Eliminate the Expensive Log Pipeline
0× storage overhead
See Pricing

Correlate Logs with Metrics Instantly
80% faster MTTR
See Unified Observability

Query Terabytes Without Performance Degradation
1M entry sampling budget
Learn About Scalability

Centralize Logs Without Losing Control
Gap-free replication
Explore Centralization

Empower Every Engineer with AI Insights
Natural language queries
Try AI Troubleshooting

How Netdata Compares
Netdata vs Traditional Log Management
See why organizations choose Netdata for systemd-journal log management
Capability
Netdata
Traditional Tools
Query Performance
✅ Sub-2 seconds
Direct journal file access
⚠️ 5-60 seconds
Pipeline latency and indexing delays
Sample Budget
✅ 1M entries
200× larger sample size
⚠️ 5K entries
Limited sampling accuracy
Storage Overhead
✅ 0× duplication
Queries journals in place
❌ 3-5× duplication
Raw + index + storage copies
Configuration Required
✅ Zero
Auto-discovery and dashboards
❌ Extensive
Shippers, parsers, indexes, dashboards
Query Language
✅ Point-and-click
No DSL or syntax to learn
❌ Complex DSL
KQL, LogQL, or custom syntax
Metrics Integration
✅ Native
Unified timeline with auto-correlation
⚠️ Separate tools
Manual correlation required
Data Sovereignty
✅ Complete
Logs never leave infrastructure
⚠️ Limited
Data shipped to external systems
AI Assistant Access
✅ Via MCP
Natural language queries
⚠️ Limited
Vendor-specific AI features
Pricing Model
✅ Flat per-node
Logs Monitoring (querying logs in place) not billed
❌ Volume-based
Costs scale with log volume
Netdata's Edge-Native Advantages
Eliminate the Entire Log Pipeline
Traditional tools require log shippers, message queues, indexers, and storage clusters - each adding latency, cost, and failure points. Netdata queries journal files directly where they live, eliminating all pipeline complexity while delivering faster results.
No data movement = 90% cost reduction
Learn About Architecture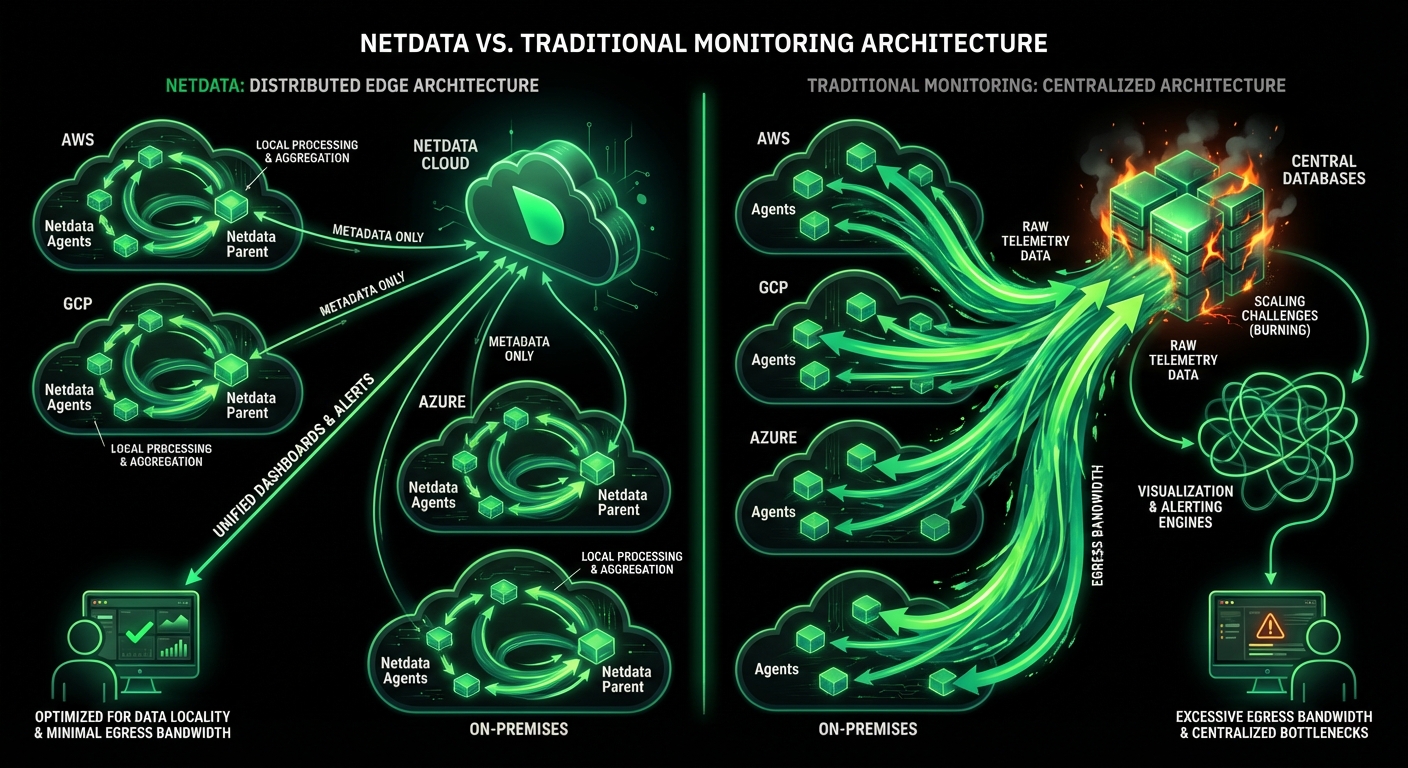

Key Takeaways
Why organizations choose Netdata for systemd-journal log management
Sub-2-Second Queries
Query terabytes of journal data in seconds with intelligent sampling and direct file access - no pipeline delays or indexing overhead.
90% Cost Reduction
Eliminate expensive log infrastructure by querying journals in place. No Elasticsearch, no Splunk, no data duplication - just direct access.
Zero Configuration
Production-ready in 60 seconds with auto-discovery, algorithmic dashboards, and point-and-click filtering - no query languages required.
Unified Observability
Metrics and logs in one synchronized timeline. Click any timeframe on a chart, and logs filter instantly - correlation is automatic and visual.
AI-Powered Insights
Ask natural language questions about logs via Model Context Protocol. Get instant root cause analysis correlated with metrics and anomalies.
Data Sovereignty
Logs never leave your infrastructure. Query journals in place with read-only access, FSS support, and TLS encryption for centralization.
November 3, 2023
System Operators: The Role Of SysOps In IT Infrastructure
See how systemd-journal and Netdata simplify log management for system operators, taming log overload without costly tools. Read the full guide now!
October 24, 2023
Improve Your Security With systemd-journal & Netdata
Learn how to leverage systemd journal logs with Netdata to strengthen Linux system security and boost operational awareness. Read the full guide now!
October 12, 2023
Exploring systemd journal logs with Netdata
Explore, search, and analyze systemd journal logs with Netdata's journal plugin for deeper system insights and faster troubleshooting. Read the guide now!