



 Observability for CISOs
Detect Infrastructure Threats in Real-Time, Not Hours Later
Netdata delivers per-second infrastructure observability with ML-based anomaly detection on every metric. Catch resource-based attacks, crypto mining, and anomalies instantly - while reducing MTTR by 80% and costs by 90% compared to traditional SIEMs.

Security Operations Excellence Through Infrastructure Intelligence
Purpose-built for security-conscious operations teams
Instant Threat Detection
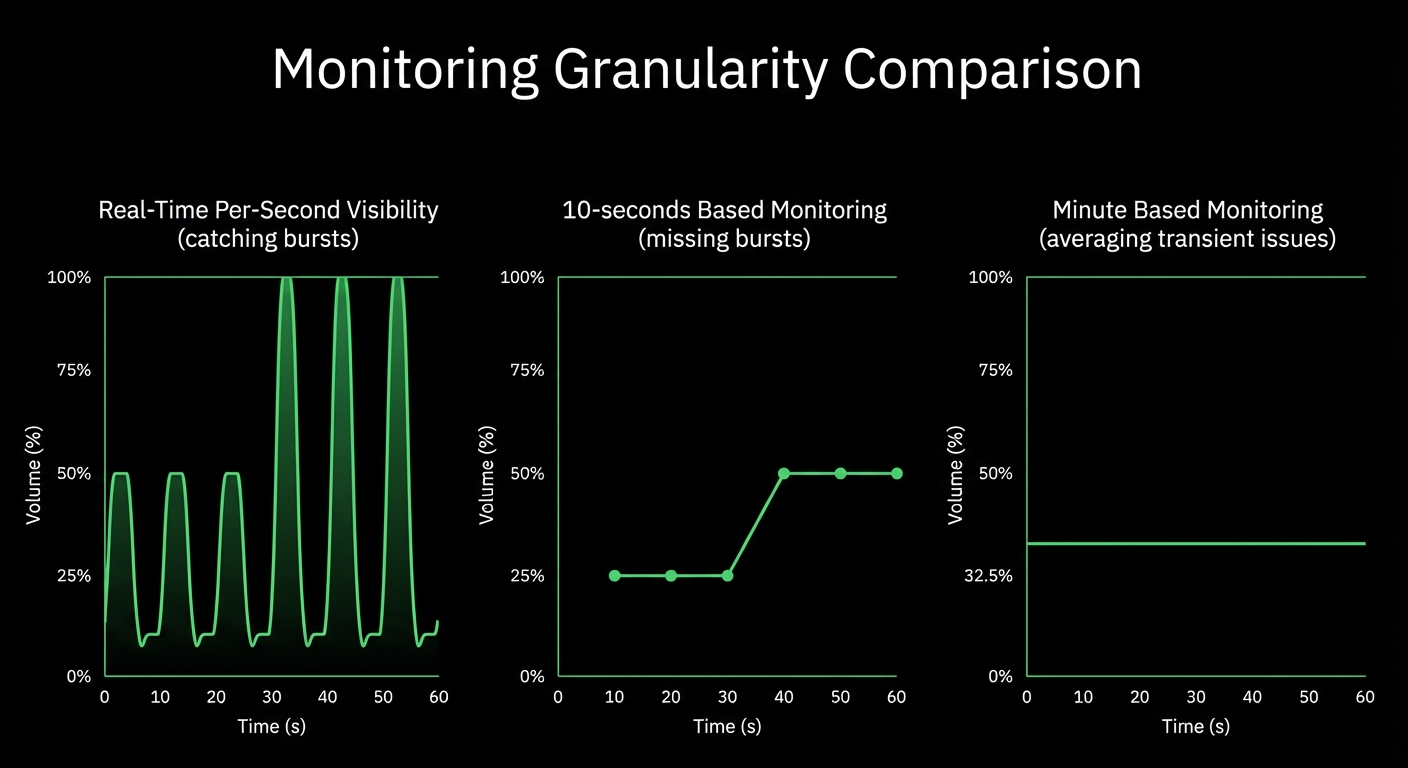
Per-second ML anomaly detection catches resource-based attacks, crypto mining, and DoS attempts invisible to minute-level monitoring - with 80% faster MTTR.
Complete Data Sovereignty
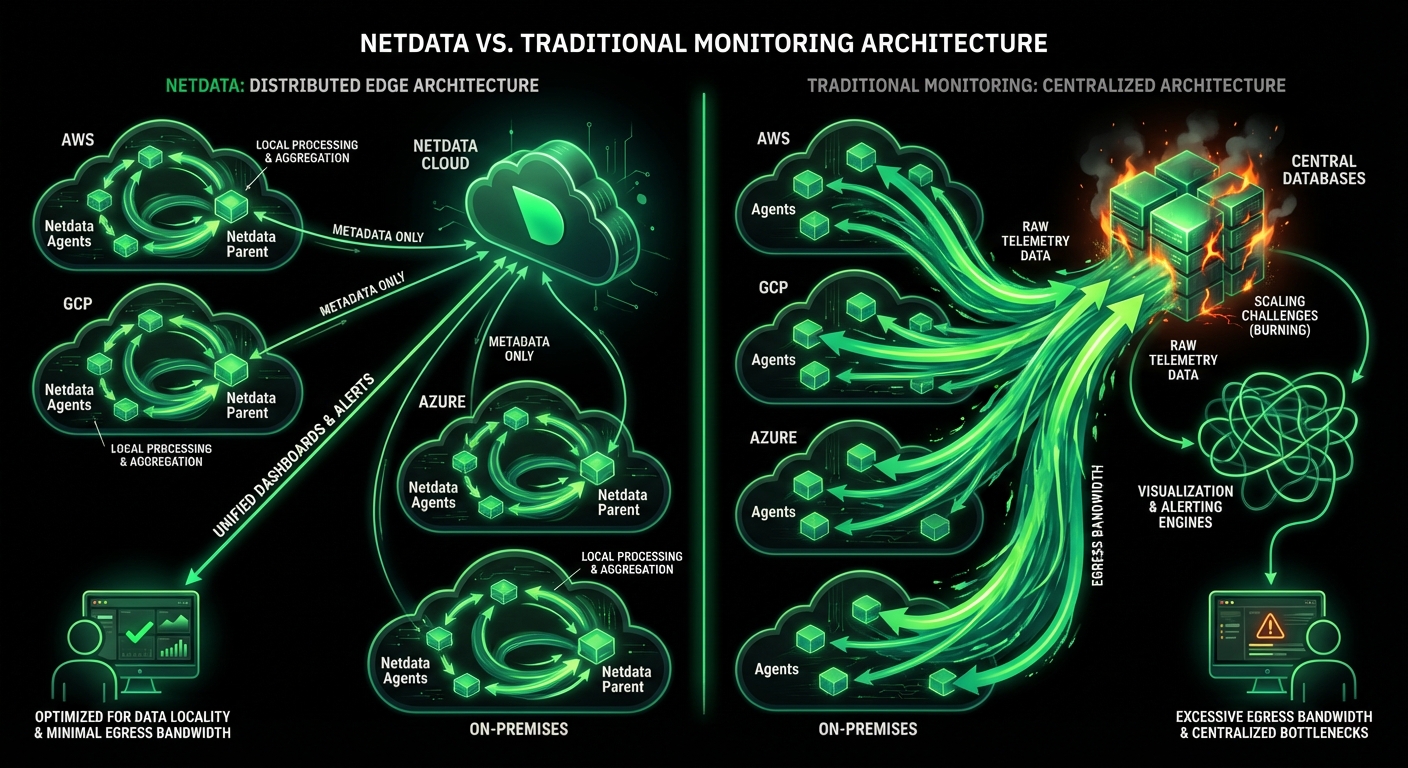
All observability data stays on-premises. SOC 2 Type 2 certified, with systemd-journal Forward Secure Sealing (FSS) for journal tamper detection. Supports GDPR, CCPA, PCI DSS, and HIPAA programs.
Root Cause in Seconds
Anomaly Advisor correlates thousands of metrics to surface the top 30-50 relevant signals, revealing cascading failures and blast radius automatically.
90% Cost Reduction
Predictable per-node pricing, with no charges for metrics volume, Logs Monitoring (querying logs in place), users, data retention or containers. No surprise bills from metrics volume spikes.
Zero Learning Curve
No query languages, no dashboard building, no specialized training. Junior engineers operate at senior-level effectiveness from day one with AI assistance.
Console Replacement
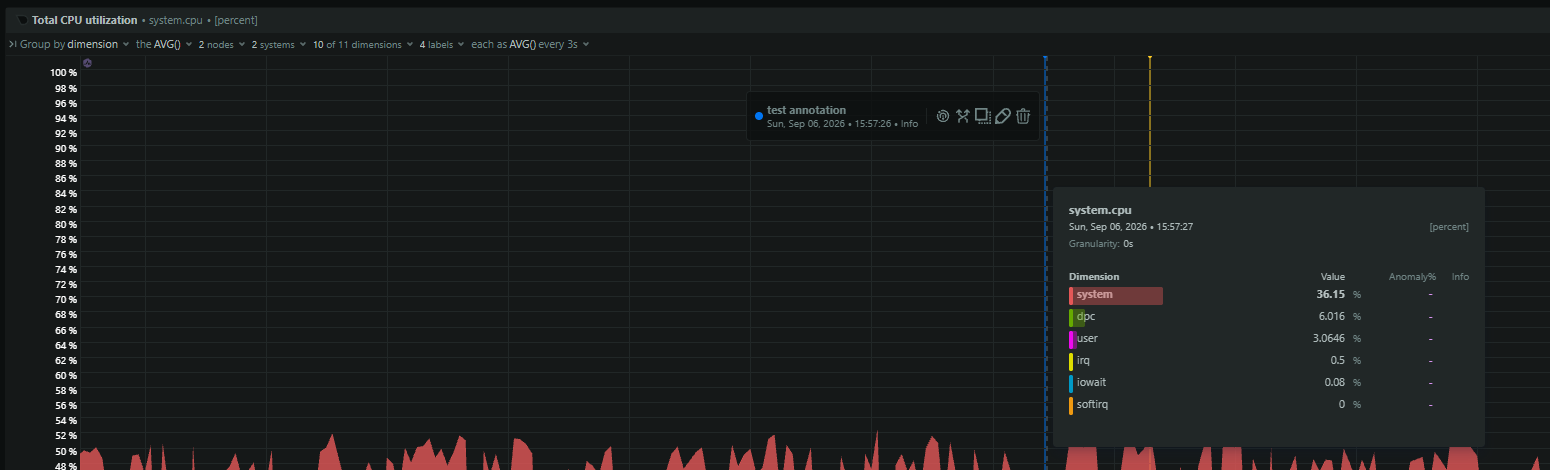
Browser-based access to all system diagnostics with history and ML. Same per-second precision as SSH tools - without infrastructure access requirements.
Trusted by security-conscious organizations worldwide







Transform Security Operations with Infrastructure Intelligence
See Every Infrastructure Anomaly as It Happens
80% MTTR Reduction
Explore Real-Time Monitoring

Eliminate Tool Sprawl and Operational Burden
Zero Configuration
Learn About Zero Configuration


Accelerate Incident Response with AI-Powered Analysis
Sub-2-Second Latency
Discover AI Features


Maintain Complete Data Sovereignty and Compliance
100% Data Locality
Review Security Design

Scale Infrastructure Security Without Cost Explosions
90% Cost Savings
See Pricing Details


Unify Visibility Across Hybrid and Multi-Cloud
800+ Integrations
Explore Cloud Support


Netdata vs. Traditional Security Monitoring
Purpose-Built for Modern Security Operations
Netdata delivers infrastructure security monitoring with real-time performance, ML-based detection, and transparent economics - without the complexity and cost of traditional SIEMs.
Capability
Netdata
Traditional SIEM
Data Granularity
✅ Per-Second
Real-time infrastructure visibility
⚠️ Per-Minute
Misses transient attacks
Anomaly Detection
✅ Every Metric
18 ML models, 99% FP reduction
⚠️ Selected Metrics
Manual tuning required
Deployment Time
✅ 60 Seconds
Zero configuration required
❌ Days to Weeks
Extensive setup and tuning
Learning Curve
✅ None
No query languages needed
❌ Advanced
SPL, KQL, specialized training
Data Sovereignty
✅ 100% On-Premises
All data stays local
❌ Cloud-Based
Data egress required
Cost Model
✅ Per-Node
Per-node pricing, no per-metric charges
❌ Per-GB/Event
Unpredictable volume charges
Alert Quality
✅ Component-Level
Accurate, actionable alerts
❌ Generic Thresholds
High noise, manual tuning
Query Performance
✅ 0.11 Seconds
16× faster than alternatives
⚠️ Minutes
Slow at scale
Log Management
✅ Advanced
OS logs in place + any source via OpenTelemetry, 90% cost reduction
❌ Pipeline Required
Elasticsearch/Splunk infrastructure
Total Cost of Ownership
✅ 90% Lower
Predictable, transparent
❌ Expensive
Hidden costs, complexity
Comprehensive Infrastructure Security Monitoring
Catch Threats Others Miss
18 unsupervised ML models per metric train automatically with zero configuration. Ensemble consensus achieves 99% false positive reduction while detecting crypto mining, resource abuse, and DoS attempts in real-time.
Theoretical 10^-36 false positive rate
Learn About ML Architecture


Security Operations Excellence
Purpose-built capabilities for modern security teams
Zero Trust Monitoring
Track network connections per process, authentication events, and certificate expiry - supporting continuous verification and zero trust architectures.
Container Security
Auto-discover and monitor containers, pods, and Kubernetes workloads with per-second resource tracking and automatic lifecycle management.
Kernel-Level Visibility
eBPF provides per-process network connections, syscalls, and I/O on bare metal and VMs - without application instrumentation.
Access Monitoring
Per-user resource tracking, login/logout events via logs, and Cloud RBAC with SSO support (OIDC, Okta, SCIM 2.0).
Multi-Cloud Security
Unified visibility across AWS, Azure, GCP, and on-premises with auto-discovery of cloud resources and native integration.
Blast Radius Detection
Anomaly Advisor automatically identifies cascading failures and impact spread across infrastructure during incidents.
Audit Logging
Comprehensive audit trails, and systemd-journal Forward Secure Sealing (FSS) for journal tamper detection - supporting compliance and forensic investigations.
Synthetic Monitoring
HTTP endpoint checks, TCP port monitoring, DNS queries, and certificate expiry tracking for external service validation.

October 5, 2026
Distributed Tracing In Netdata: OpenTelemetry Traces
Netdata now ingests OpenTelemetry traces over OTLP on the same Agent that collects your metrics and logs. Spans are stored and indexed on your own infrastructure and explored in the new Traces tab in Netdata Cloud.

October 3, 2026
Who Built This Dashboard, and Are They Still Here?
Your server monitoring dashboard shouldn't be a DIY project. Netdata charts every metric automatically — no query languages, no dashboards to build, ever.
September 8, 2026
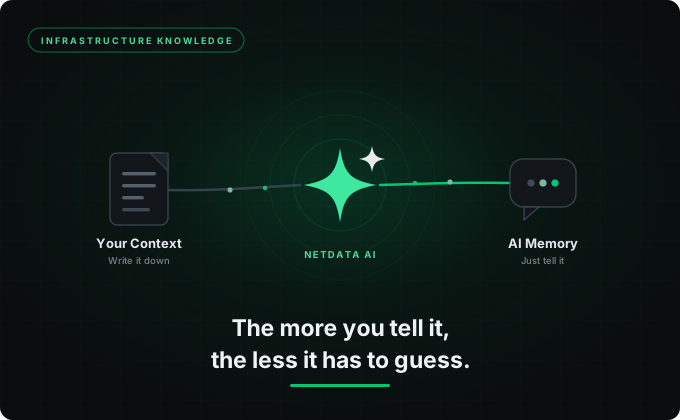
Infrastructure Knowledge For AI Root Cause Analysis
Netdata AI now learns your infrastructure the way a new SRE would: a shared context document your team writes, and a memory layer built from conversations that gets more accurate every time you use it.