-
-
 Semgrep Code
Find and fix the issues that matter in your code (SAST)
-
 Semgrep Supply Chain
Fix vulnerabilities in open source dependencies and block malware
-
 Semgrep Secrets
Find and fix hardcoded secrets with semantic analysis
-
 Semgrep Guardian
Scan and fix AI-generated code the moment it's written
-
 Multimodal
Combine AI reasoning with rule-based analysis for detection, triage, and remediation
-
 Semgrep AppSec Platform
Automate, manage, and enforce security across your organization
-
 Semgrep Workflows
Build and deploy security pipelines that combine static analysis with AI at scale
-
-
-
 Open-Source Malware Protection
Protect against software supply chain attacks
-
 Static application security testing
Increase security while accelerating development
-
 OWASP Top 10
Prevent the most critical web application security risks
-
 Secure Guardrails
Protect Your Code with Secure Guardrails
-
 Fintech
Mitigate software supply chain risks
-
SaaS & Cloud
Increase security while accelerating development
-
-
-
 Docs
Want to read all the docs? Start here
-
 Blog
Get the latest news about Semgrep
-
ROI Calculator
See how Semgrep can save you time and money
-
 Community Slack
Join the friendly Slack group to ask questions or share feedback
-
Events
Join us at a Semgrep Event!
-
Case Studies
See why users love Semgrep
-
Video Library
View our library of on-demand webinars
-
-


Code Security
for Builders and Agents
Catch, flag, and fix real vulnerabilities before they ship, powered by security that learns as you build. Unify SAST, SCA, secrets scanning, and malware protection into one platform built for today’s software era.
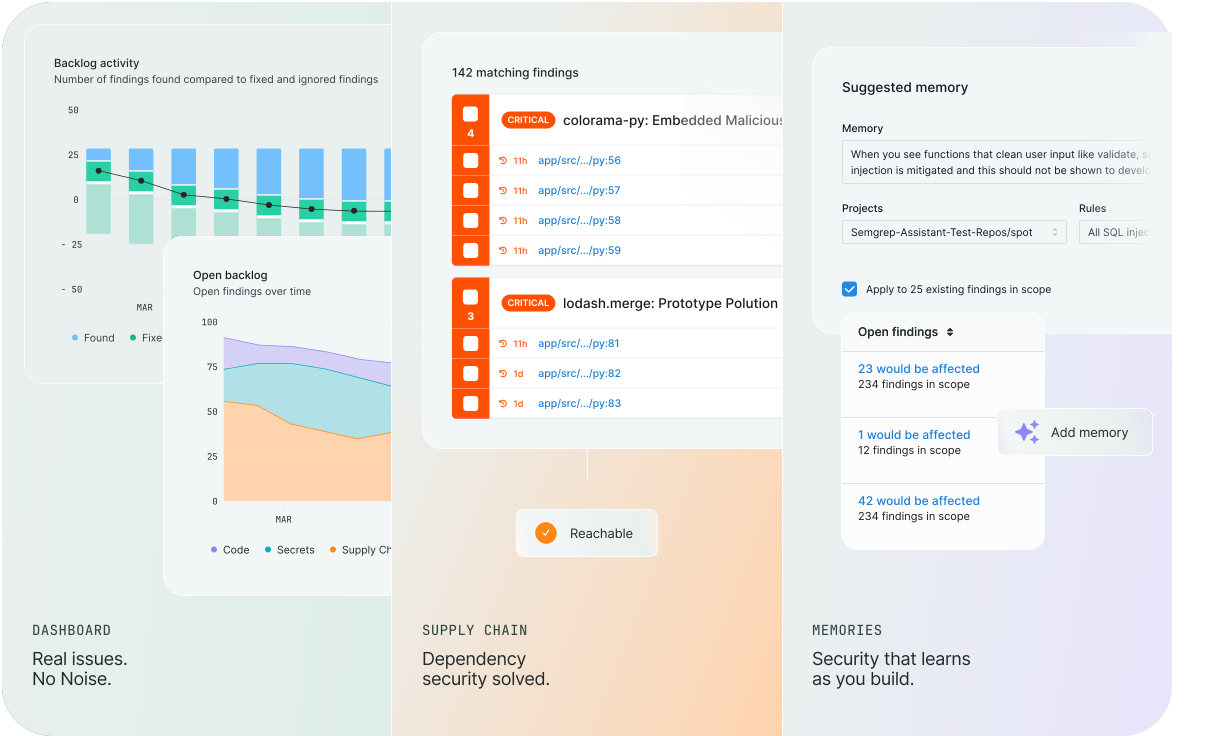





Built for Builders, Trusted by Security
Lives where developers work, delivering fixes without breaking flow. Gives security teams visibility, control, and confidence.
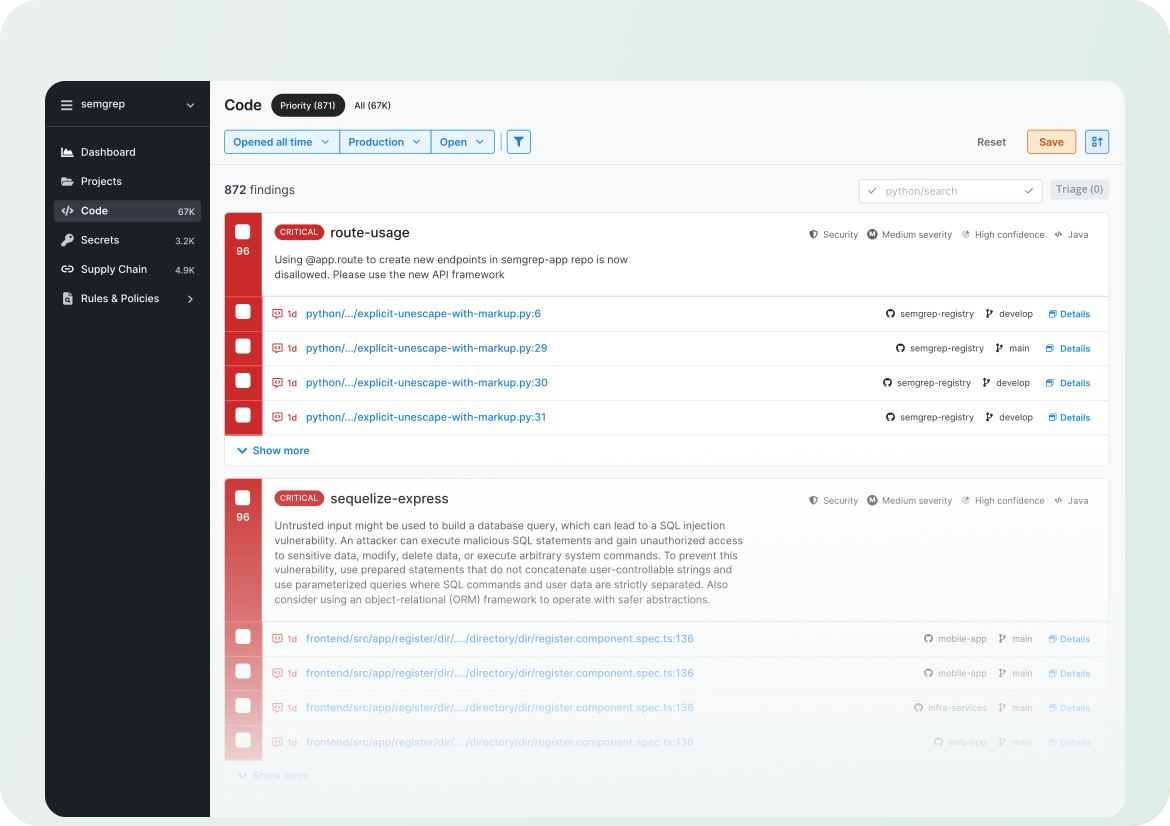

Empower invention without friction
Industry-leading SAST, SCA, and secrets scanning in one high signal AppSec platform.

Prevention at the Source
Secure code as it’s written. Built-in guardrails guide safe fixes before code ships.

Make Zero False Positives a Reality
AppSec teams triage 80% fewer false positives across SAST and SCA. Backlogs shrink, and engineering velocity climbs.

Smarter as You Build
AI learns your code context to eliminate false positives and prioritize reachable vulnerabilities – validated by 95% of security reviewers across 6M+ findings.
End-to-End Open Source Malware Protection
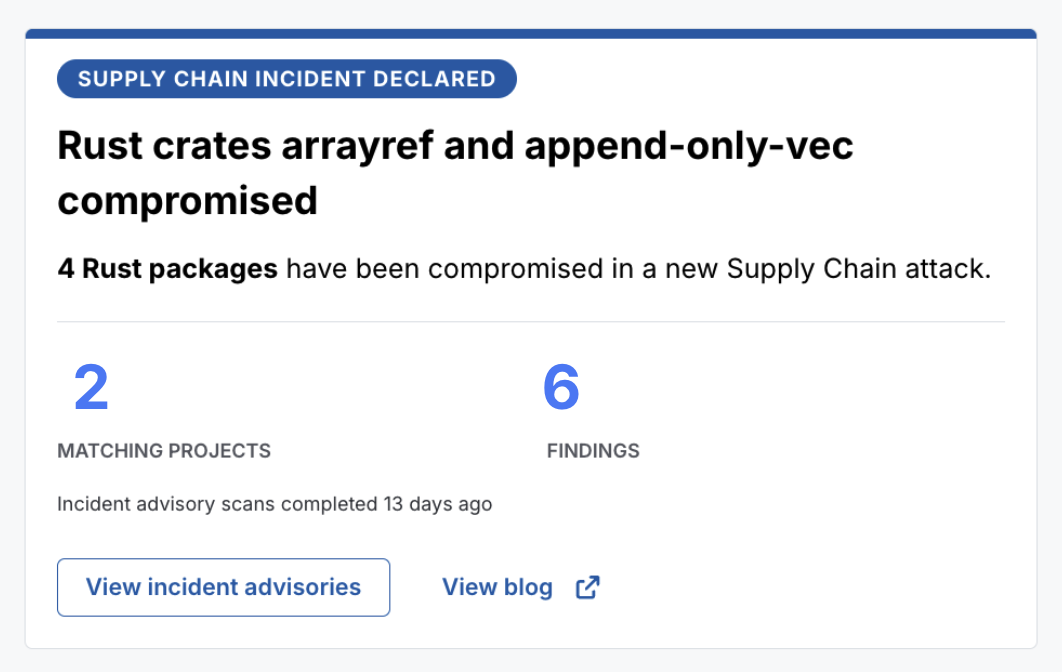
Zero-Day Incident Detection
24/7 on-call security monitoring triggers an incident scan within 30 minutes of discovery. Teams get notified by Semgrep and can see the latest malware findings on their dashboard or via API.
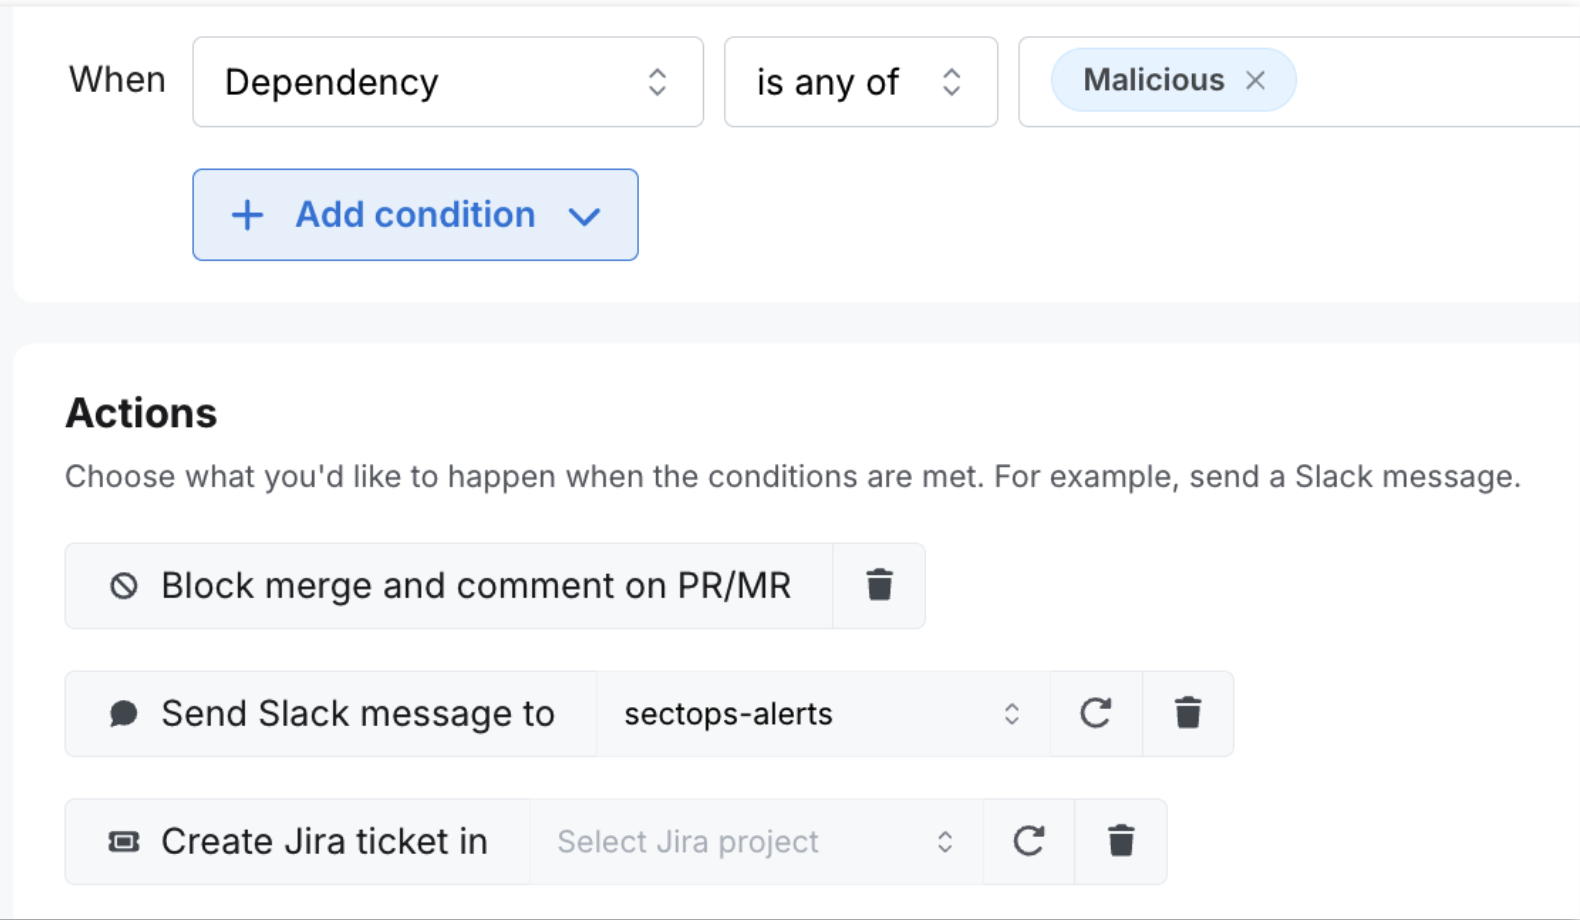
Org-wide IR automation
Enterprise-grade policies, with Slack and JIRA integration, take malware findings and trigger predefined remediation workflows, for end-to-end incident response automation.
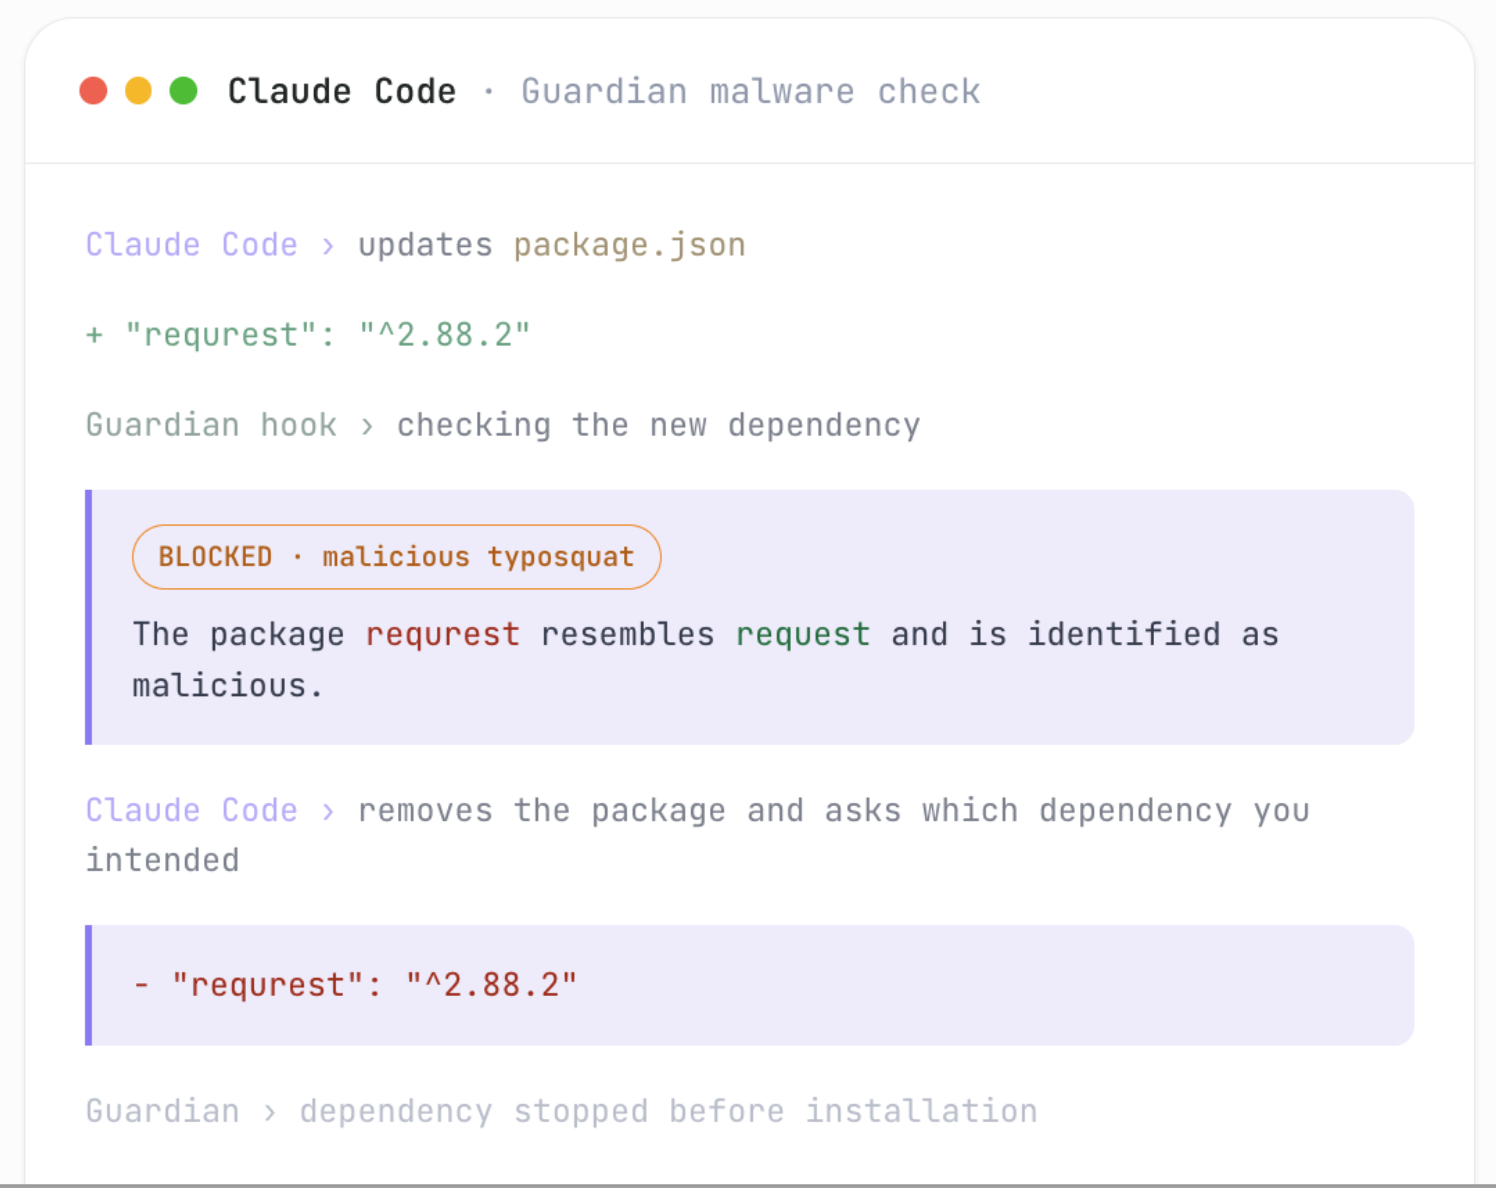
Malware Firewall
Semgrep Malware Firewall runs silently on developer machines, intercepting network requests to any public registry and blocking malicious and compromised open-source packages from reaching your environment.
AI woven across the AppSec lifecycle
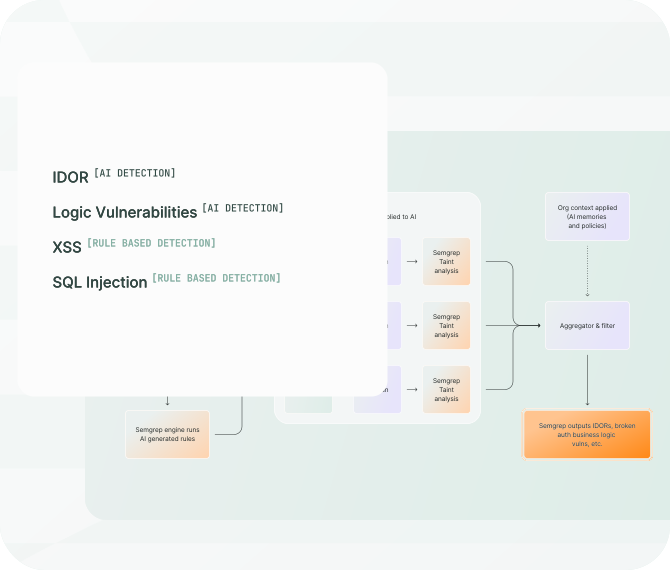
Detect What Matters
Detect complex issues like IDORs, broken authorization, and multi-step logic flaws.
Combine deterministic static analysis with AI reasoning to understand naming, structure, and developer intent – going beyond pattern matching.
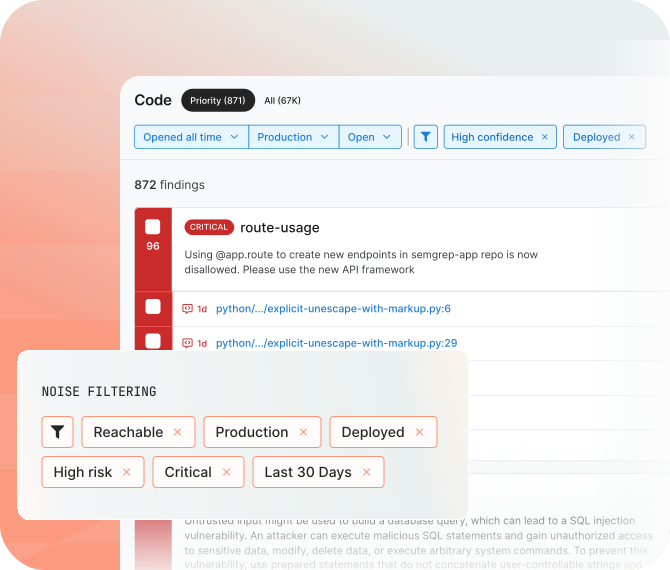
Noise Filtering
Prioritize what matters. Eliminate what doesn’t. Automatically triage findings using code context, patterns, and prior decisions.
Provisionally ignore false positives so AppSec teams focus on real risk. Don’t audit alerts. Automate them away.
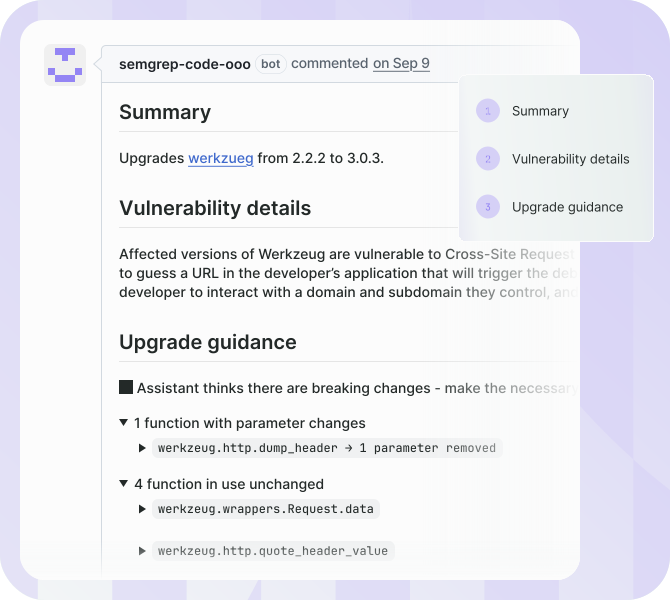
Remediation
Turn findings into safe, actionable fixes – fast. Generate tailored remediation and upgrade guidance directly in PRs and IDEs.
Security stops being a blocker. Developers fix issues safely with confidence, not guesswork.
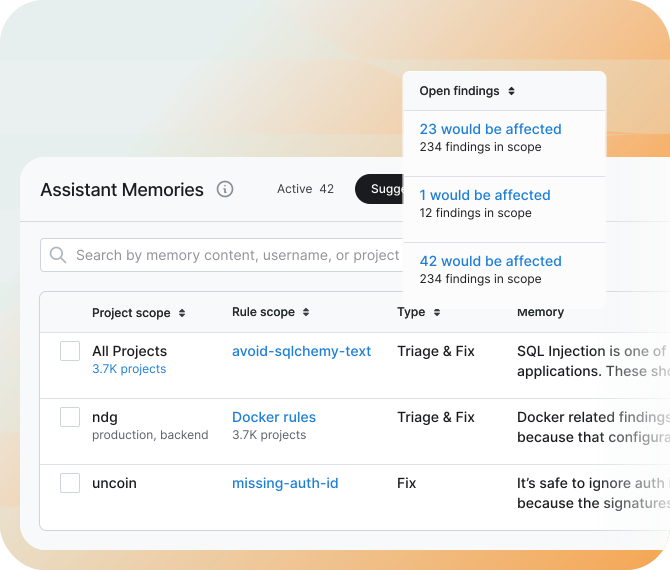
Prevention
Learn once, prevent forever. Human triage decisions create reusable “memories” that suppress repeat false positives automatically. Signal compounds over time. False positives don’t come back.
Works where you build. Connects where your software runs
Supported workflows and integrations:
- CLI, CI/CD, and IDEs (VS Code, JetBrains)
- PR checks in GitHub, GitLab, Bitbucket, Azure
- Jira and ticketing workflow routing
- APIs and webhooks
- MCP integrations for AI tools like Cursor and Replit
- Cloud context via partners including Palo Alto Networks, Sysdig, StackHawk
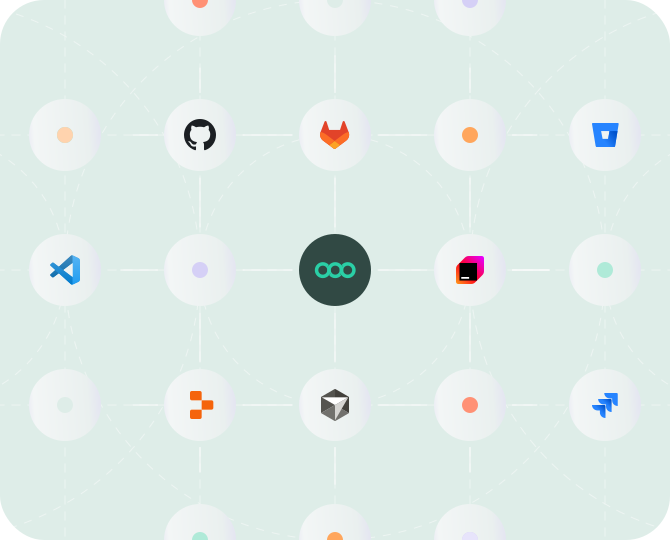
Code security that unifies teams, accelerates delivery, and reduces real risk
For Developers
- Clear, actionable findings
- Fix issues in PRs, CI, IDEs, or AI tools
- Ship faster with confidence
For AppSec Teams
- High signal results across SAST, SCA, and secrets scanning
- Scalable guardrails powered by rules and AI
- Less noise, real risk reduction
For CISOs
- Measurable security outcomes
- Unified visibility across humans and AI
- Proactive security without slowing the business
No buzzwords, just
real world results


"Semgrep helped surface valuable context and recommendations to developers, aiding in the quick identification of false positives and remediation of legitimate findings. There were times where it just felt magical."
“We use Semgrep to provide remediation guidance to our developers directly in PR comments. Semgrep gives them additional context that helps them fix vulnerabilities quicker.”
"The ability to have Semgrep remember what I told it and automatically triage for me in the future is game changing. I have to spend a lot of time verifying the validity of vulnerabilities and being able to essentially hit the "save" button on the work I've done and just pass it on to Semgrep has really helped streamline my triage process."
Code security for builders and agents