The Open Source Security Foundation (OpenSSF) is a community of software developers, security engineers, and more who are working together to secure open source software for the greater public good.
Collaborate on capabilities and best practices that secure open source software.
Participate in the latest community conversations and engage with experts.
Take free courses on secure coding practices as part of our certificate program.
Explore our helpful security guides to help secure your project from the start.
Members
Projects
Working Groups
What’s in the SOSS? Podcast
Recent Blog Posts
New OpenSSF Guide: Finding and Fixing Vulnerabilities Using AI
AI has gotten good at finding software vulnerabilities, and attackers are already using it. For example, “AI-enabled adversaries increased attacks by 89% year-over-year” according to the CrowdStrike 2026 Global Threat…
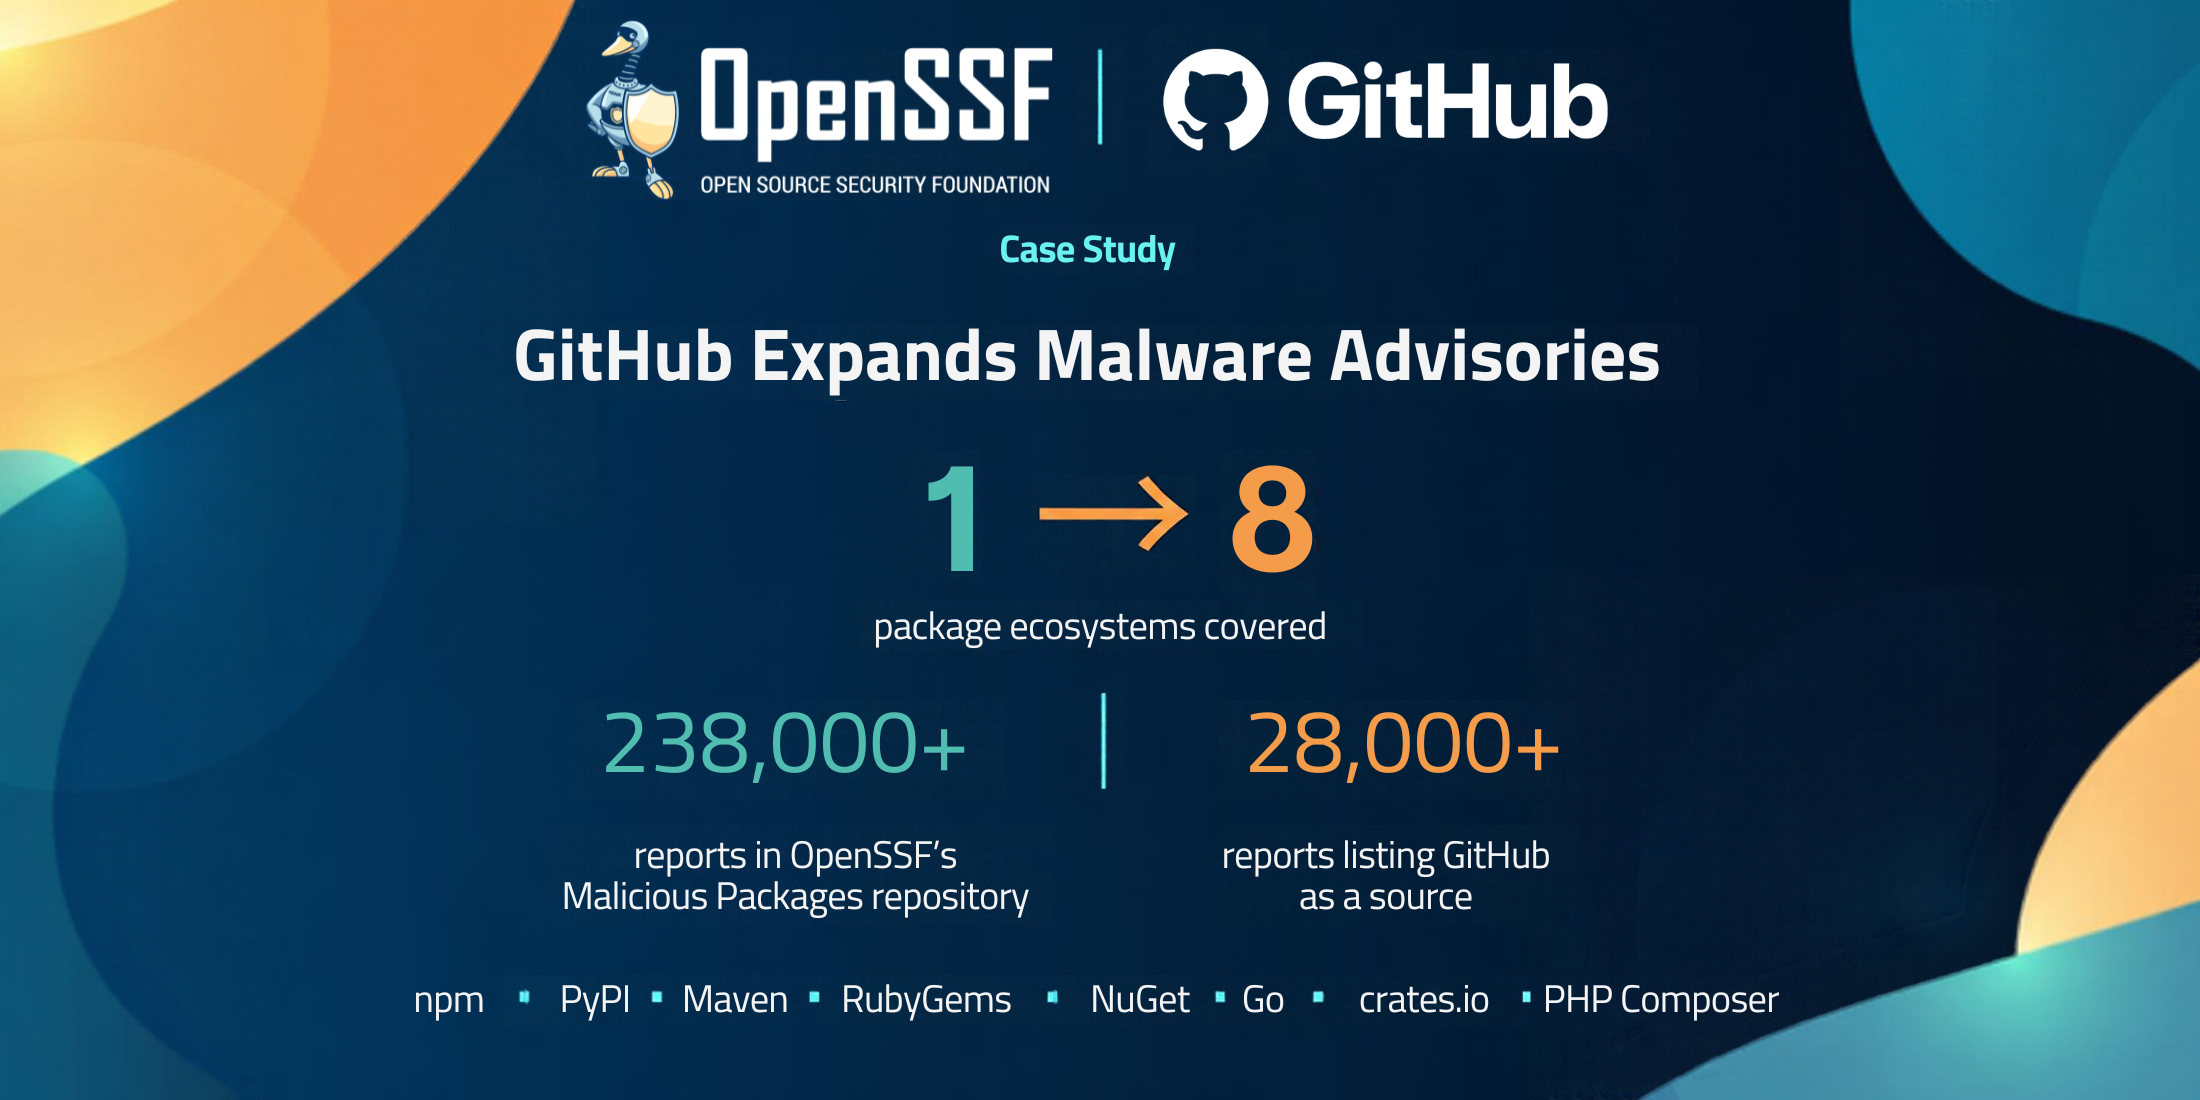
Case Study: GitHub Expands Malware Advisories Across Eight Ecosystems with OpenSSF
Learn how GitHub integrated OpenSSF's malicious-package data into its Advisory Database to expand Dependabot malware alerts across eight ecosystems.
Introducing Privateer: AI-Assisted Security & Compliance Evaluation Framework Joins the OpenSSF Sandbox
Discover Privateer, a new plugin-based, AI-assisted security and compliance evaluation framework that has officially joined the OpenSSF Sandbox under the ORBIT Working Group.
Open source software is pervasive in data centers, consumer devices, and applications. Securing open source software requires fostering collaboration, establishing best practices, and developing innovative solutions.
Join the growing list of organizations supporting the advancement of securing open source technology and funding the development and adoption of OpenSSF initiatives.

