


- Home
-
CWE-1021: Improper Restriction of Rendered UI Layers or Frames
Weakness ID: 1021Vulnerability Mapping: ALLOWED This CWE ID may be used to map to real-world vulnerabilities
Abstraction: Base Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.View customized information:For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers. For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts. For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers. For users who wish to see all available information for the CWE/CAPEC entry. For users who want to customize what details are displayed. Description
The web application does not restrict or incorrectly restricts frame objects or UI layers that belong to another application or domain. 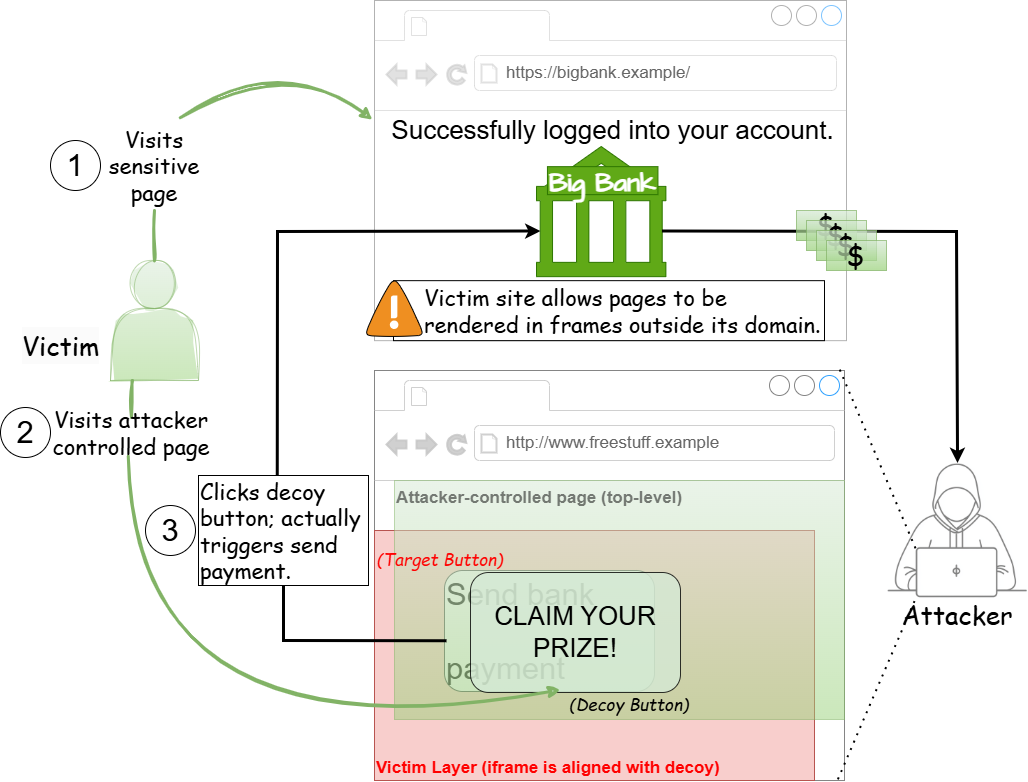 Alternate Terms
Common Consequences
 This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact Details Gain Privileges or Assume Identity; Bypass Protection Mechanism; Read Application Data; Modify Application Data
Scope: Access Control An attacker can trick a user into performing actions that are masked and hidden from the user's view. The impact varies widely, depending on the functionality of the underlying application. For example, in a social media application, clickjacking could be used to trick the user into changing privacy settings.
Potential Mitigations
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Research Concepts" (View-1000)
Nature Type ID Name ChildOf  Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
441 Unintended Proxy or Intermediary ('Confused Deputy') ChildOf
Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
451 User Interface (UI) Misrepresentation of Critical Information
Relevant to the view "Software Development" (View-699)
Nature Type ID Name MemberOf  Category - a CWE entry that contains a set of other entries that share a common characteristic.
355 User Interface Security Issues
Relevant to the view "Weaknesses for Simplified Mapping of Published Vulnerabilities" (View-1003)
Nature Type ID Name ChildOf
Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
610 Externally Controlled Reference to a Resource in Another Sphere
Modes
Of IntroductionThe different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase Note Implementation
Applicable PlatformsThis listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Languages Class: Not Language-Specific (Undetermined Prevalence)
Technologies Class: Not Technology-Specific (Undetermined Prevalence)
Class: Web Based (Undetermined Prevalence)
Selected Observed
Examples
Weakness Ordinalities Detection
Methods Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature Type ID Name MemberOf Category - a CWE entry that contains a set of other entries that share a common characteristic.1348 OWASP Top Ten 2021 Category A04:2021 - Insecure Design MemberOf Category - a CWE entry that contains a set of other entries that share a common characteristic.1396 Comprehensive Categorization: Access Control MemberOf Category - a CWE entry that contains a set of other entries that share a common characteristic.1441 OWASP Top Ten 2025 Category A06:2025 - Insecure Design
Vulnerability Mapping Notes
Related Attack Patterns References Content
History SubmissionsSubmission Date Submitter Organization 2017-08-01
(CWE 2.12, 2017-11-08)CWE Content Team MITRE  Modifications
Modification Date Modifier Organization 2026-04-30
(CWE 4.20, 2026-04-30)CWE Content Team MITRE updated Common_Consequences, Description, Diagram, Potential_Mitigations 2025-12-11
(CWE 4.19, 2025-12-11)CWE Content Team MITRE updated Applicable_Platforms, References, Relationships, Weakness_Ordinalities 2023-06-29
(CWE 4.12, 2023-06-29)CWE Content Team MITRE updated Mapping_Notes 2023-04-27
(CWE 4.11, 2023-04-27)CWE Content Team MITRE updated Detection_Factors, References, Relationships 2023-01-31
(CWE 4.10, 2023-01-31)CWE Content Team MITRE updated Related_Attack_Patterns 2021-10-28
(CWE 4.6, 2021-10-28)CWE Content Team MITRE updated Relationships 2020-08-20
(CWE 4.2, 2020-08-20)CWE Content Team MITRE updated Related_Attack_Patterns 2020-06-25
(CWE 4.1, 2020-06-25)CWE Content Team MITRE updated Potential_Mitigations 2020-02-24
(CWE 4.0, 2020-02-24)CWE Content Team MITRE updated Applicable_Platforms, Relationships 2019-06-20
(CWE 3.3, 2019-06-20)CWE Content Team MITRE updated Related_Attack_Patterns, Relationships


